
Real programme ownership at a critical moment
NIS2 and DORA are live. Eneco operates critical energy infrastructure with a broad supplier ecosystem. You are not maintaining a mature programme - you are shaping what it becomes at exactly the moment it matters most.
Influence that goes beyond security
This role puts you at the table with Procurement, Legal, Compliance, and the business. TPRM at Eneco is not a back-office function - it is a business-critical capability with executive visibility.
A mission that means something
Eneco's goal is climate neutrality by 2035. The infrastructure and supplier ecosystem you protect underpins that ambition. The work is serious, the stakes are real, and the organisation is committed.
Why choose Eneco?
Eneco is one of Europe's leading sustainable energy companies, working toward climate neutrality by 2035 through our One Planet strategy. Our Digital & Tech and Security organisation is a critical enabler of that mission - and the TPRM programme you lead sits at the heart of how we manage risk across our supplier ecosystem.
What you’ll do
- Own the TPRM framework end-to-end - policies, standards, procedures, risk registers, and playbooks
- Lead governance forums and steer risk-based decision-making and risk acceptance processes
- Define and track KPIs, KRIs, and executive dashboards that give management real visibility of supplier risk
- Drive continuous improvement across the full third-party lifecycle - from onboarding through to offboarding
Supplier Assessments and Risk Management
- Perform and oversee security assessments of new and existing suppliers - reviewing ISO 27001, SOC reports, pen test results, BCDR plans, and security controls
- Evaluate supplier cyber maturity, provide risk ratings, and define remediation requirements
- Maintain risk registers, manage exceptions, and oversee remediation tracking
- Implement continuous monitoring for critical suppliers and manage periodic reassessments
- Support supplier breach response activities alongside the incident management team
Procurement and Regulatory Integration
- Embed mandatory security review gates into procurement - high-risk vendors do not get onboarded without assessment and approval
- Support contract reviews and security clause integration alongside Legal and Procurement
- Align TPRM practices with NIS2, DORA, ISO 27001, NIST, and GDPR requirements
- Prepare evidence and reporting for internal and external audits and regulatory examinations
Platform and Automation
- Own and optimise the TPRM/GRC platform - driving automation of vendor onboarding, risk tiering, workflows, and reporting
- Identify opportunities to reduce manual effort and increase assessment coverage through tooling
- Define reporting capabilities that translate supplier risk data into actionable management insight
Is this about you?
You are a senior TPRM professional who has built or significantly matured a third-party risk programme in a complex enterprise environment. You know how to assess a supplier, but more importantly you know how to design a programme that scales, earns organisational trust, and keeps pace with a shifting regulatory landscape. You are comfortable in a room with senior stakeholders, confident presenting risk data to the board, and able to push back constructively when a high-risk vendor is being fast-tracked without proper scrutiny.
Experience
- 5+ years hands-on experience in Third Party Risk Management
- 7+ years in Cyber Security, IT Risk, Information Security, or GRC
- Proven track record leading or maturing a TPRM programme in a large enterprise
- Experience influencing senior stakeholders and embedding security controls into procurement and supplier governance processes
- Familiarity with critical infrastructure or regulated sector environments is a strong plus
Knowledge and Expertise
- Deep understanding of TPRM frameworks - vendor risk assessments, risk tiering, continuous monitoring, fourth-party risk, supply chain security, and exception management
- Strong knowledge of relevant regulations and standards - NIS2, DORA, ISO 27001, NIST CSF, GDPR
- Hands-on experience with at least one GRC/TPRM platform - ServiceNow GRC, OneTrust, Archer, ProcessUnity or similar
- Solid grounding in information security domains - cloud security, identity and access management, incident management, and BCDR
Skills and Competencies
- Ownership mindset - you take accountability for the programme, not just the tasks
- Executive presence - you communicate risk clearly to senior stakeholders and translate complexity into decisions
- Analytical and data-driven - you use risk data to drive prioritisation, not just report status
- Automation mindset - you look for ways to increase coverage and reduce manual effort through tooling and process design
- Collaborative - you influence across Legal, Procurement, Risk, IT, and Business without formal authority
Certifications (preferred)
- CISSP, CISM, or CRISC
- ISO 27001 Lead Implementer or Lead Auditor
- Certified Third Party Risk Professional (CTPRP) is a strong plus
You’ll be responsible for
Eneco operates critical energy infrastructure and depends on a broad ecosystem of technology suppliers and service partners. As that ecosystem grows in complexity, so does the risk it carries - and regulators are paying close attention. NIS2 and DORA are not future considerations here. They are operational realities.
As TPRM Lead you own the end-to-end Third Party Risk Management programme - from framework and governance through to supplier assessments, continuous monitoring, and procurement integration. This is not an assessment execution role. You are here to mature the programme, increase its organisational reach, and make third-party cyber risk visible and manageable at every level of the business.
You will work from within the CISO Office, partnering with Procurement, Legal, Compliance, Risk, Data Privacy, and IT. You will need to influence without formal authority - and you will have the mandate to do it.
This is where you’ll work
You will be part of the CISO Office at Eneco, working within a security organisation that sits at the intersection of a major energy transition and a rapidly evolving regulatory environment. Your stakeholders span Procurement, Legal, Compliance, Enterprise Risk, Data Privacy, IT, and the wider business - giving you broad organisational reach from day one.
Eneco operates critical infrastructure and is directly in scope for NIS2 and DORA. That gives the TPRM programme real weight - and gives you a genuine mandate to drive change. We work hybrid, combining focused days from home with collaboration at Eneco's Rotterdam HQ.
What we have to offer

Gross annual salary between €72,000 and €90,100

FlexBudget

Personal and professional growth

Hybrid working: home, office or abroad
Want more information about our terms of employment?
Work Where Everyone Matters
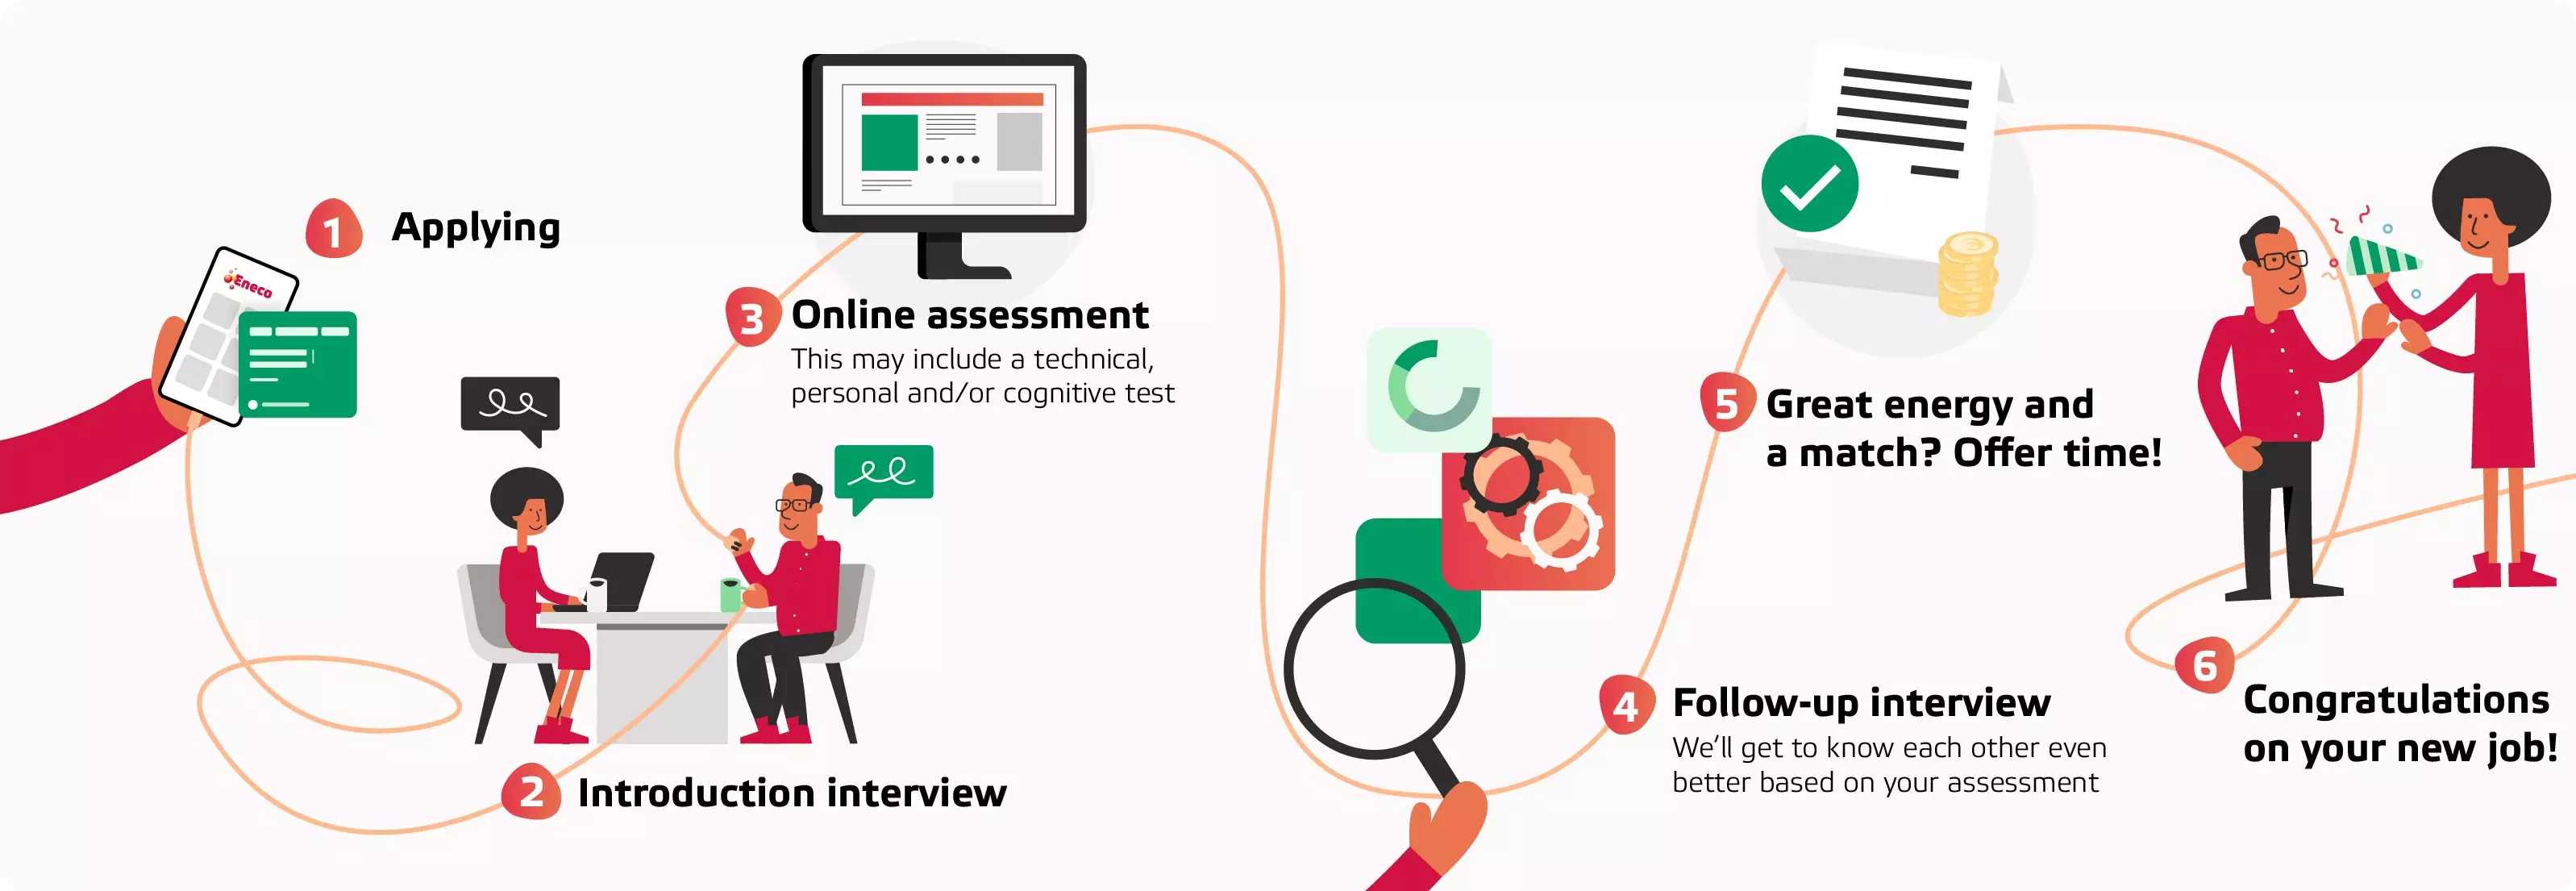
The phases of our application procedure
Want to know more about this job function?
Please apply directly via the Eneco Careers Portal. Applications submitted by email will not be processed.
Third Party Disclaimer
Eneco manages recruitment through selected channels and preferred partners. Unsolicited acquisition, candidate submissions, or commercial outreach in relation to this vacancy are not appreciated.

Questions about the application procedure
Donja Huidar
Would you like to receive our newest job vacancies?
This website uses cookies
For the proper functioning and anonymous analysis of our website, we place necessary and functional cookies,
which have no consequences for your privacy.
We use more cookies, for example to make our website more relevant to you,
to make it possible to share content via social media and to show you relevant advertisements on third-party websites.
These cookies may collect data outside of our website. By clicking "Accept" By clicking you agree to the placing of these cookies.
You can find more information in our cookie policy.