
The timing is the opportunity. Eneco is mid-transformation: cloud modernisation is running, OT environments are expanding, major platform decisions are being made right now. None of those decisions currently have a security architecture voice in the room. You arrive at exactly the moment when what you define will actually become the standard — because the patterns are not set yet. In two years, this will be an established function. Right now, it is a blank page.
You are the first. There is no Security Architect at Eneco. The function does not exist yet — and neither does an enterprise architecture layer above it. You are not inheriting a framework, a governance model, or a set of standards. You are building all of it from scratch, at a company that operates critical energy infrastructure across IT and OT, with NIS2, DORA, and an accelerating cloud and digital transformation already in motion. That combination — full mandate, no ceiling, genuinely consequential scope — is rare at any organisation of this scale.
IT and OT — both, at real scale. Most security architect roles sit firmly on one side of that line. This one crosses it. Eneco's estate covers enterprise IT, cloud platforms, and operational technology in critical energy infrastructure — and the security architecture needs to work across all of it. If you have spent your career wanting to work at the intersection of digital transformation and OT security, without the compromise of doing only one half, this is that role.
Why choose Eneco?
Eneco is one of Europe's leading sustainable energy companies, committed to climate neutrality by 2035 through our One Planet strategy. We are electrifying heating, mobility, and industry at scale — and the technology that supports that ambition is growing at the same pace as the ambition itself.
Security architecture at Eneco is not a compliance checkbox. It sits at the intersection of a major IT and OT transformation, the protection of critical national infrastructure, and a regulatory environment — NIS2, DORA, GDPR — that is only becoming more demanding. The decisions made here are consequential in a way that most security roles are not: energy infrastructure, smart grid technology, OT environments, cloud platforms, and real-time trading systems. And unlike most organisations of this scale, Eneco does not yet have a Security Architect or an enterprise architecture function. You are not joining an established practice — you are founding one.
What you’ll do
As Senior Security Architect, you combine deep technical expertise with architectural authority and business influence. You define the security blueprint across IT, OT, cloud, applications, and supplier ecosystems — and you make sure it is actually adopted. You own the standards, run the reviews, and act as the lead security voice in every major programme and platform initiative.
You drive security-by-design across the organisation, from cloud platform patterns to DevSecOps practices, from OT reference architectures to third-party integration requirements. You identify the gaps between where Eneco is today and where the security architecture needs to be, and you translate that into a roadmap the organisation can execute.
Is this about you?
You are a builder, not an inheritor. You have set up security architecture functions before — or you have operated in environments where you had to create the structure yourself because no one else was going to. You know how to establish a governance process from zero, write the first reference architecture before anyone asks for it, and earn credibility with engineering teams who have never had a security architect in the room before.
You are equally at home on the IT and OT side of the line. You understand the difference between a cloud platform decision and an industrial control system risk, and you know how to communicate both to a CISO, a platform engineer, and an operations team in the same week. You balance technical rigour with business pragmatism — you know when to hold the line on a standard and when a compensating control is the right call. You do not need a framework handed to you. You build the framework.
Required experience
- Minimum 7 years in cybersecurity, information security, security engineering, or security architecture
- Minimum 3 years in a dedicated Security Architect, Lead Security Engineer, or Enterprise Security Architect role
- Experience designing security architectures across complex enterprise environments — IT, OT, cloud, application, and supplier ecosystems
- Experience supporting major transformation, cloud migration, modernisation, or critical infrastructure programmes
- Demonstrated ability to influence and challenge senior business and technology stakeholders
Technical knowledge
- Enterprise security architecture and security-by-design
- Cloud security — primarily Microsoft Azure; AWS and hybrid cloud experience valued
- Network, endpoint, infrastructure, and platform security
- Identity and access management and zero-trust architecture
- Application security, API security, secure SDLC, and DevSecOps
- Data security, classification, encryption, and privacy-by-design
- OT / ICS security architecture — ISA/IEC 62443 preferred
- Third-party and supply chain security
- Vulnerability management, security monitoring, and detection
- Business continuity, cyber resilience, and risk management
Frameworks & regulatory knowledge
- ISO/IEC 27001 and ISO/IEC 27002
- NIST Cybersecurity Framework
- CIS Controls
- NIS2 and applicable national cybersecurity legislation
- GDPR
- ISA/IEC 62443 (preferred)
- DORA (where applicable)
Preferred certifications
- CISSP
- SABSA
- TOGAF
- CISM
- CCSP
- Microsoft Azure security or solutions architecture certifications
- GIAC security certifications
- ISO 27001 Lead Implementer or Lead Auditor
You’ll be responsible for
Security Architecture & Design
- Define and own enterprise security architecture principles, standards, reference architectures, and design patterns across IT, OT, cloud, and application domains
- Develop solution security architectures for major technology initiatives, platforms, and transformation programmes
- Embed secure-by-design and secure-by-default principles into every layer of the technology estate
- Maintain a current target-state security architecture aligned to business strategy and regulatory requirements
Governance & Assurance
- Establish and operate security architecture review processes and governance forums
- Review solution designs, technology implementations, and architectural exceptions — including risk-based compensating controls
- Assess alignment with security policies, standards, risk appetite, NIS2, DORA, GDPR, and applicable regulation
- Provide clear, risk-based recommendations that senior business and technology stakeholders can act on
Programmes, Projects & Change
- Act as lead security architect for strategic programmes, platform migrations, and major technology changes
- Conduct architecture and design reviews at every stage of the project lifecycle
- Integrate security requirements into procurement, development, implementation, and operational processes
- Validate that controls are appropriately designed, implemented, and effective
Cloud & Infrastructure Security
- Define secure cloud architecture patterns and implementation guidance — primarily Azure, including hybrid and SaaS contexts
- Lead adoption of zero-trust, identity-centric, and modern security architecture principles
- Develop reusable security standards for infrastructure and platform engineering teams
- Review network, endpoint, and infrastructure solutions against security architecture standards
Application & Data Security
- Define secure application architecture requirements, API security standards, and data protection controls
- Embed security within the software development lifecycle and DevSecOps practices
- Provide privacy-by-design and data classification requirements across technology programmes
- Review application and integration designs for security risks and architectural alignment
OT / ICS Security Architecture
- Develop and maintain OT security reference architectures for Eneco's operational technology environments
- Support engineering teams in securing industrial control systems and critical infrastructure
- Assess vendor and solution compliance with OT security requirements, including ISA/IEC 62443 where applicable
- Ensure security architecture requirements align with safety, resilience, and operational availability constraints
Third-Party & Supply Chain Security
- Define security architecture requirements for third-party integrations, managed services, cloud providers, and external connections
- Support the TPRM team with architectural assessments, technical risk evaluation, and remediation guidance
- Review architectures associated with suppliers and strategic partners
Roadmap & Continuous Improvement
- Identify architectural gaps, technical debt, and security improvement opportunities across the estate
- Contribute to multi-year security architecture roadmaps and capability development initiatives
- Track emerging technologies, threat developments, and industry best practice
- Provide thought leadership on future-state security architecture, resilience, and control maturity
This is where you’ll work
You join Eneco's CISO Office within the Digital & Tech domain, embedded in the Security Architecture & Engineering team. You work across the full technology estate — cloud infrastructure, OT environments, application development, and supplier ecosystems — as the architectural authority on security.
The role connects you directly with enterprise architects, engineering leads, programme managers, and senior business stakeholders. You will operate at both strategic and technical levels: defining the target-state architecture, running the governance forums, and getting into the design detail when it matters. Eneco's hybrid working model is based in Rotterdam, with the flexibility to work where you deliver the most impact.
This is a senior individual contributor role with real influence. You are the expert in the room — and you will be expected to act like it.
What we have to offer

Gross annual salary between €82,000 and €110,000

FlexBudget

Personal and professional growth

Hybrid working: home, office or abroad
Want more information about our terms of employment?
Work Where Everyone Matters
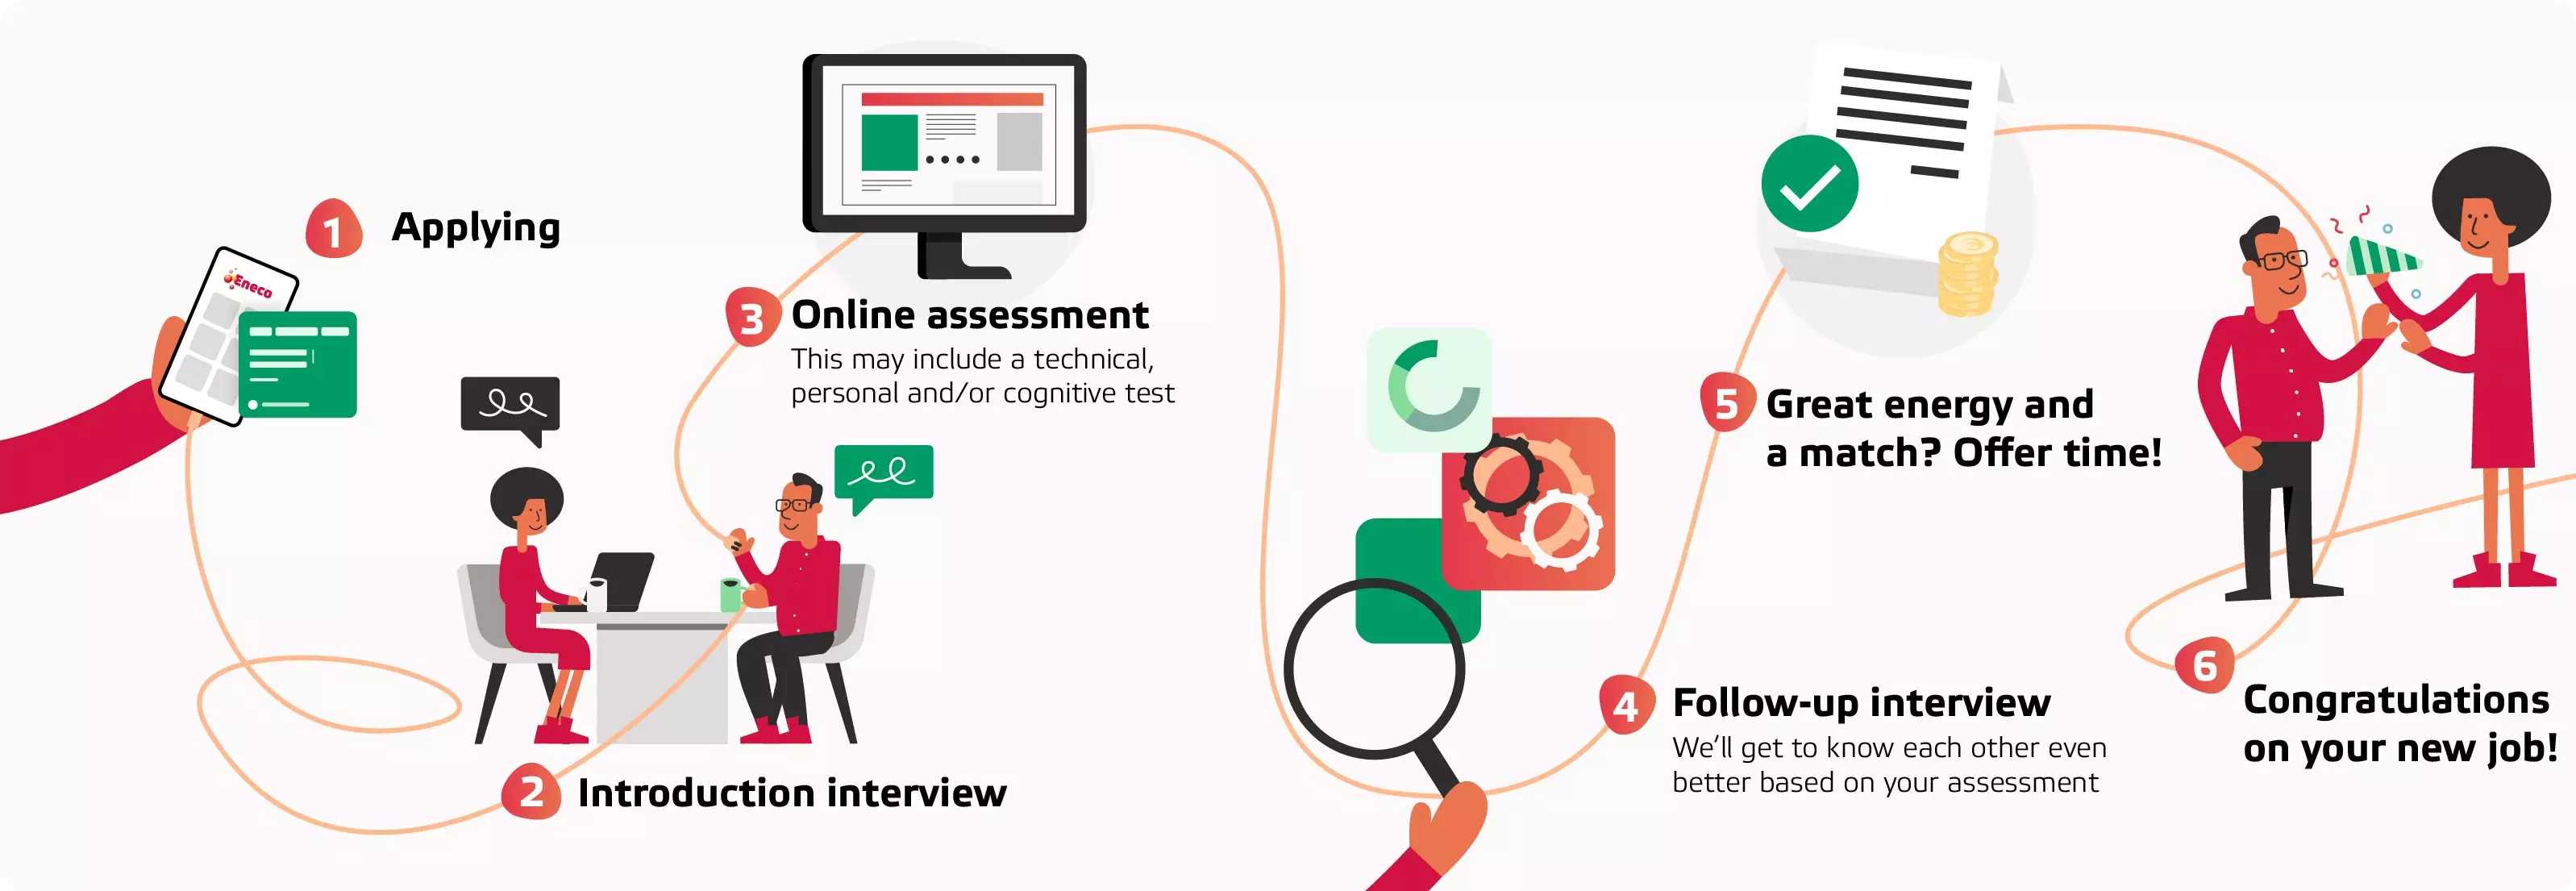
The phases of our application procedure
Want to know more about this job function?
Apply directly via the Eneco Careers Portal. Applications submitted by email or LinkedIn will not be processed.
Third Party Disclaimer
Eneco manages recruitment through selected channels and preferred partners. Unsolicited acquisition, candidate submissions, or commercial outreach in relation to this vacancy are not appreciated.
Questions about the application procedure
Donja Huidar
Would you like to receive our newest job vacancies?
This website uses cookies
For the proper functioning and anonymous analysis of our website, we place necessary and functional cookies,
which have no consequences for your privacy.
We use more cookies, for example to make our website more relevant to you,
to make it possible to share content via social media and to show you relevant advertisements on third-party websites.
These cookies may collect data outside of our website. By clicking "Accept" By clicking you agree to the placing of these cookies.
You can find more information in our cookie policy.